Videos
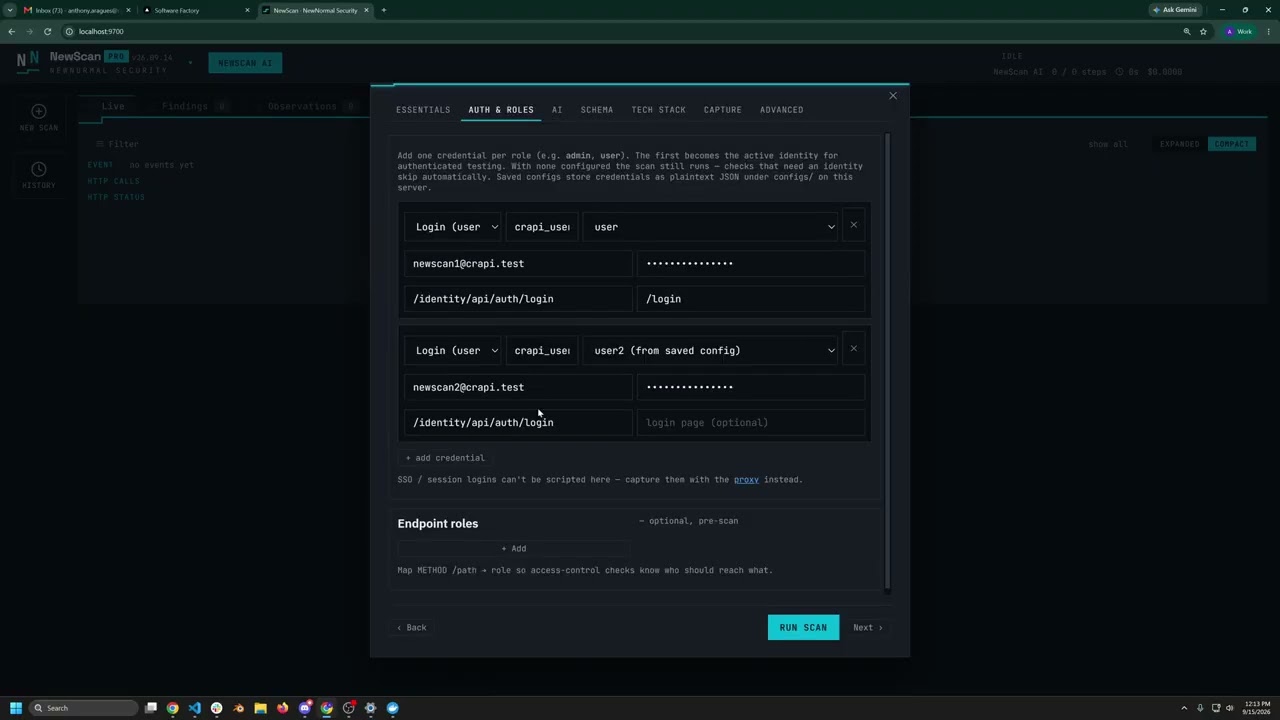
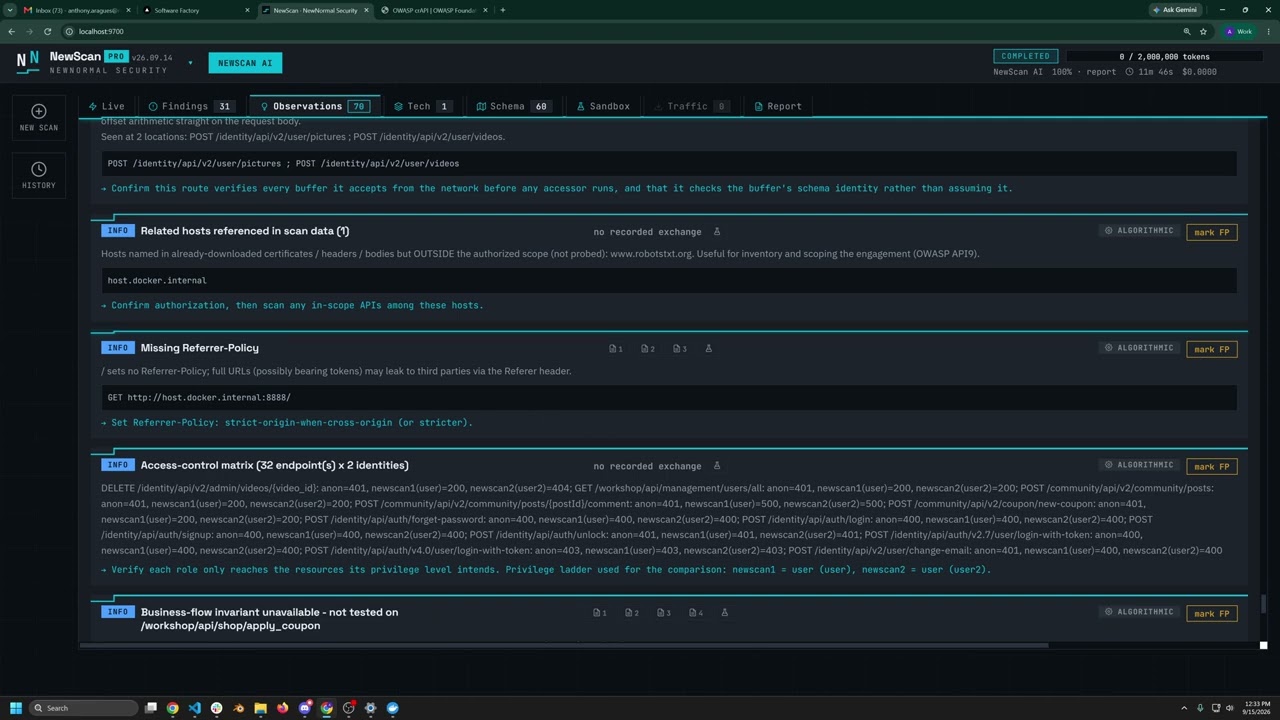
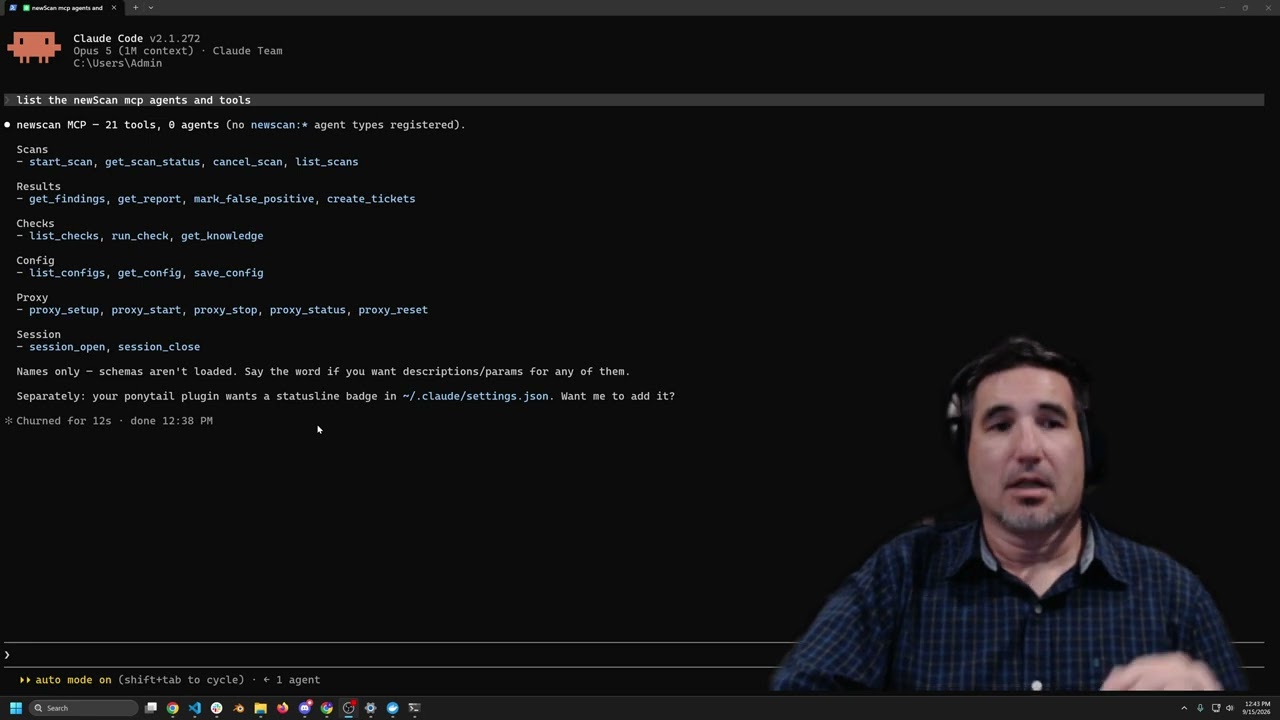
Overview
// free · local · verifies every findingNewScan is a free, self-hosted scanner that sweeps your whole engagement — APIs, web apps, network & infrastructure, Wi-Fi, and segmentation — and re-runs every hit to confirm it's real before reporting it. A deterministic floor runs with no key; an optional AI layer (BYOK) goes deeper. Everything runs on your box.
- →Free to self-host in the browser console — no license, seat fees, or demo call to scan your APIs, web apps and networks locally. API, CLI, MCP and CI/CD automation need NewScan Pro.
- →Local-first — target traffic, findings, and AI keys never leave your machine.
- →Evidence-backed findings — every finding is reproduced and cross-referenced before it's recorded, with the evidence attached and severity never inflated.
- →AI optional, BYOK — fully deterministic with no key; add OpenAI / Anthropic / Gemini / Ollama for deeper reach.
- →CI-ready with Pro — SARIF 2.1.0 plus a severity exit-code gate for any pipeline.
- →Compliance-calibrated — one score mapped to PCI DSS, SOC 2, ISO 27001, HITRUST, HIPAA, and NIST 800-53.

FINDINGS
Confirmed findings ranked by severity, each with reproduced evidence and remediation attached.

WEB SCAN
The live web-app scan — crawl, probe, and verify in a real browser, streamed step by step.

TECH STACK
The detected technology stack and infrastructure, fingerprinted from responses and cross-referenced to known CVEs.
Use AI where it makes the scan better
// deterministic proof · agentic reach · your choiceNewScan starts with a complete deterministic scan, then uses AI for the work where judgement and iteration add reach. Every AI-led signal is still checked against real evidence before it becomes a finding. Run without AI, bring your own model, use NewScan AI, or let your own agent drive the loop.
MCP / YOUR AGENT · PRO
Give your agent the controls
With NewScan Pro, the local MCP server lets any MCP-capable agent start scoped scans, run checks, read evidence and reports, fix your code, then rescan until the gate passes. Your agent chooses the workflow; NewScan supplies the scanning control plane.
BUILT-IN AGENTS
Go beyond the fixed sweep
Built-in ReACT and campaign agents use the deterministic results, near-misses and shared scan knowledge to plan high-yield follow-ups, craft target-specific probes and investigate attack paths. An adversarial pass tries to refute the result before it is recorded.
AI ON YOUR TERMS
Choose how it runs
Quick and baseline profiles need no model or key. For AI-assisted depth, bring an OpenAI, Anthropic, Gemini, Ollama or compatible-provider key and keep it local, or use integrated NewScan AI with pay-as-you-go billing. The scan engine and evidence bar stay the same.
Want the full agent loop? Install a NewScan Pro license, then connect NewScan to your MCP client →
Scan types
// five surfaces, one toolAPI
REST · GraphQL · gRPC · SOAP · MCP · WebSocket
WEB
SPA crawl (Playwright) · XSS · SSTI · CSRF
NETWORK
hosts · ports · TLS · DNS · SMB/SNMP · CVE
WI-FI
rogue APs, device ID & client posture
SEGMENTATION
cross-VLAN reachability · PCI CDE
Findings are shared across modes — a network scan hands discovered web services straight to the API scanner, so nothing falls between tools.
Detections categories
// high level · OWASP API / Web / LLM Top 10ACCESS CONTROL
BOLA / IDOR · function-level · business-flow abuse
AUTHENTICATION
JWT inspection · weak-secret cracking
INJECTION
SQLi · cmdi · SSTI · XSS · NoSQL · XXE · Prompts
SSRF
server-side request forgery
DATA EXPOSURE
secrets / PII · mass assignment (BOPLA)
DATA EXFILTRATION
out-of-band egress · blind SSRF/XXE callbacks · DNS/webhook exfil
NETWORK & INFRA
TLS / cert · DNS & email · SMB/SNMP · CVE cross-ref
AI / LLM
LLM01 prompt injection · MCP tool poisoning
BROWSER & SESSION TRUST
CSRF · clickjacking · CORS · cookie flags · open redirect · tabnabbing · XS-Leak
BUSINESS LOGIC
race conditions · value tampering · workflow limits
DENIAL OF SERVICE
open resolvers · UDP amplification · resource exhaustion
Plus CRLF injection, file-upload and cloud-storage exposure, deserialization, SAML/OAuth misconfiguration, dependency & CVE cross-referencing, and cross-finding attack-chain correlation. Out-of-band classes (blind SSRF, OOB SQLi/XXE, blind XSS) unlock with NewScan Pro.
Want the exact payloads and checks for your stack? The technology breakdowns go detector-by-detector on GraphQL, gRPC, SOAP, Spring Boot, Kubernetes, JWT/OAuth, MongoDB, Redis, Supabase, Firebase, WordPress, Next.js and AI-backed APIs.
Protocols
// tested natively, not just RESTREST
HTTP / HTTPS APIs
OpenAPI / Postman / HAR import · full injection & auth testing
GRAPHQL
Dedicated GraphQL pack
engine fingerprinting · introspection abuse · batching / DoS · CSRF & injection
gRPC
HTTP/2 + protobuf
reflection discovery · mTLS transport audit · per-field fuzzing
WEBSOCKET
Live channel testing
CSWSH · origin validation · authenticated message-level fuzzing
MCP
AI tool servers
tool poisoning · unauthenticated exposure · indirect prompt injection
SOAP
Auto-detected
classified by content-type / WSDL, tested through the injection engine
Authentication schemes
// scan authenticated, as a real userBEARER / JWT
bare tokens auto-prefixed; JWTs inspected for weak signing
API KEY
custom header (default X-API-Key) on every request
HTTP BASIC
username : password, Base64 Authorization header
OAUTH2
client-credentials & password grants, token auto-installed
FORM / SPA LOGIN
API login or browser-driven (Playwright) session capture
HMAC SIGNING
per-request HMAC-SHA256/512 with a shared secret
On the roadmap: session cookie · mTLS client certificates · OAuth2 authorization-code + PKCE.
Reports & exports
// one scan, every format your workflow needsSARIF
SARIF 2.1.0
Machine-readable results for CI code-scanning — GitHub, Azure DevOps, and any SARIF-aware pipeline, with a severity exit-code gate.
MARKDOWN
Markdown report
A human-readable write-up to review or hand to stakeholders — prints or converts to PDF cleanly.
INTERACTIVE TRIAGE
Self-contained HTML
Per-finding status & notes, severity filtering, and one-click Jira / GitHub tickets — triage in the report itself.
HAR
HAR traffic capture
The scan's raw HTTP requests and responses — replay and inspect every exchange in Burp or browser DevTools.
Run it in CI/CD — or from your agent
// NewScan Pro · scan a release before you shipLocal in-band scanning through the browser console is free — including pointing it at an API as the target. API, CLI, MCP and CI/CD automation require an active NewScan Pro license. Install it once in the console (Settings → License) or pass it as NEWSCAN_LICENSE_KEY. An AI provider key is separate: the keyless profiles skip the AI layer, not the license. See NewScan Pro pricing →
AS AN MCP SERVER · PRO
With a NewScan Pro license installed, the running app serves an MCP server on the same port, so any MCP-capable agent can scan, read the findings, fix the code and rescan until the gate passes. Two commands and you're driving it from Claude Code:
$ docker compose up            # the app, console and /mcp on http://localhost:9700
$ claude mcp add --transport http newscan http://127.0.0.1:9700/mcp

> Using the newscan MCP server, scan http://localhost:3000, then fix each
  real finding in this repo and rescan until nothing high or above is left.
Any other client: add an HTTP / streamable-HTTP server at the same URL. Full tool reference and the scan → fix → rescan loop in the MCP docs.
AS A SCRIPT · PRO
With NewScan Pro, NewScan runs headless with a single command and exits with a severity gate code, so any pipeline can scan a build and fail it before deploy — no server, no browser. The keyless quick profile needs no AI provider key; it still needs the Pro license.
$ export NEWSCAN_LICENSE_KEY=…   # your NewScan Pro license
$ python -m newscan https://staging.example.com \
    --scan-mode api --profile quick \
    --fail-on high --sarif out.sarif
Exit 0 clean · 1 a finding met the threshold · 2 the scan couldn't run, including no active license. SARIF uploads straight to GitHub/GitLab code scanning.
GITHUB ACTIONS
Or use the NewScan Action — one step, no install, SARIF into the Security tab. Point it at a preview deploy or an app you start as a job service; make it a required check and a PR can't merge until it passes.
permissions:
  security-events: write   # upload-sarif needs this
  contents: read

steps:
  - uses: NewNormal-Security/newscan-action@v1
    with:
      target: https://staging.example.com
      license: ${{ secrets.NEWSCAN_LICENSE }}
      fail-on: high
  - if: always()
    continue-on-error: true
    uses: github/codeql-action/upload-sarif@v4
    with: { sarif_file: newscan.sarif }
The SARIF upload needs code scanning enabled — free on public repos, GitHub Advanced Security on private ones — so it is marked continue-on-error: a repo without it still passes, and the gate itself already fails the job on findings. Inputs, outputs and three ready workflows (deploy gate, ephemeral service, per-PR preview) are in the action's README. The action and the script above both need NewScan Pro; scanning through the browser console stays free.