PHP is only the latest example of the problem, your language could be next.
Oct 24, 2026 #php2shell #blackoctober
PHP isn't the problem.
PHP has had an unfortunate week. This isnt the the only critical vulnerability they've had but it's one of the worst. These vulnerabilities and their attacks are going to come more frequently. Accelerated by 2 factors:
- More code is being generated faster and looser than ever before. AI has enabled non developers to create apps that sovle real world problems. That is amazing. But they arent very aware of good and bad programming patterns and they don't have the experience that led to the old addage of "All code is bad code, less code is better" and similar sentiments. They aren't very aware of how their app is created, only what it does.
- AI is finding vulnerabilities at scale. Whether it's through accessing and analyzing code, or testing vulnerabilities through probing / fuzzing it can more thoroughly find and test for vulnerabilities at a scale beyond what people have the time to.
You can see the jump in the CVEs over time, where there's the bump in vulnerabilities reported when AI became mainstream, and then a huge explosion as they got better.
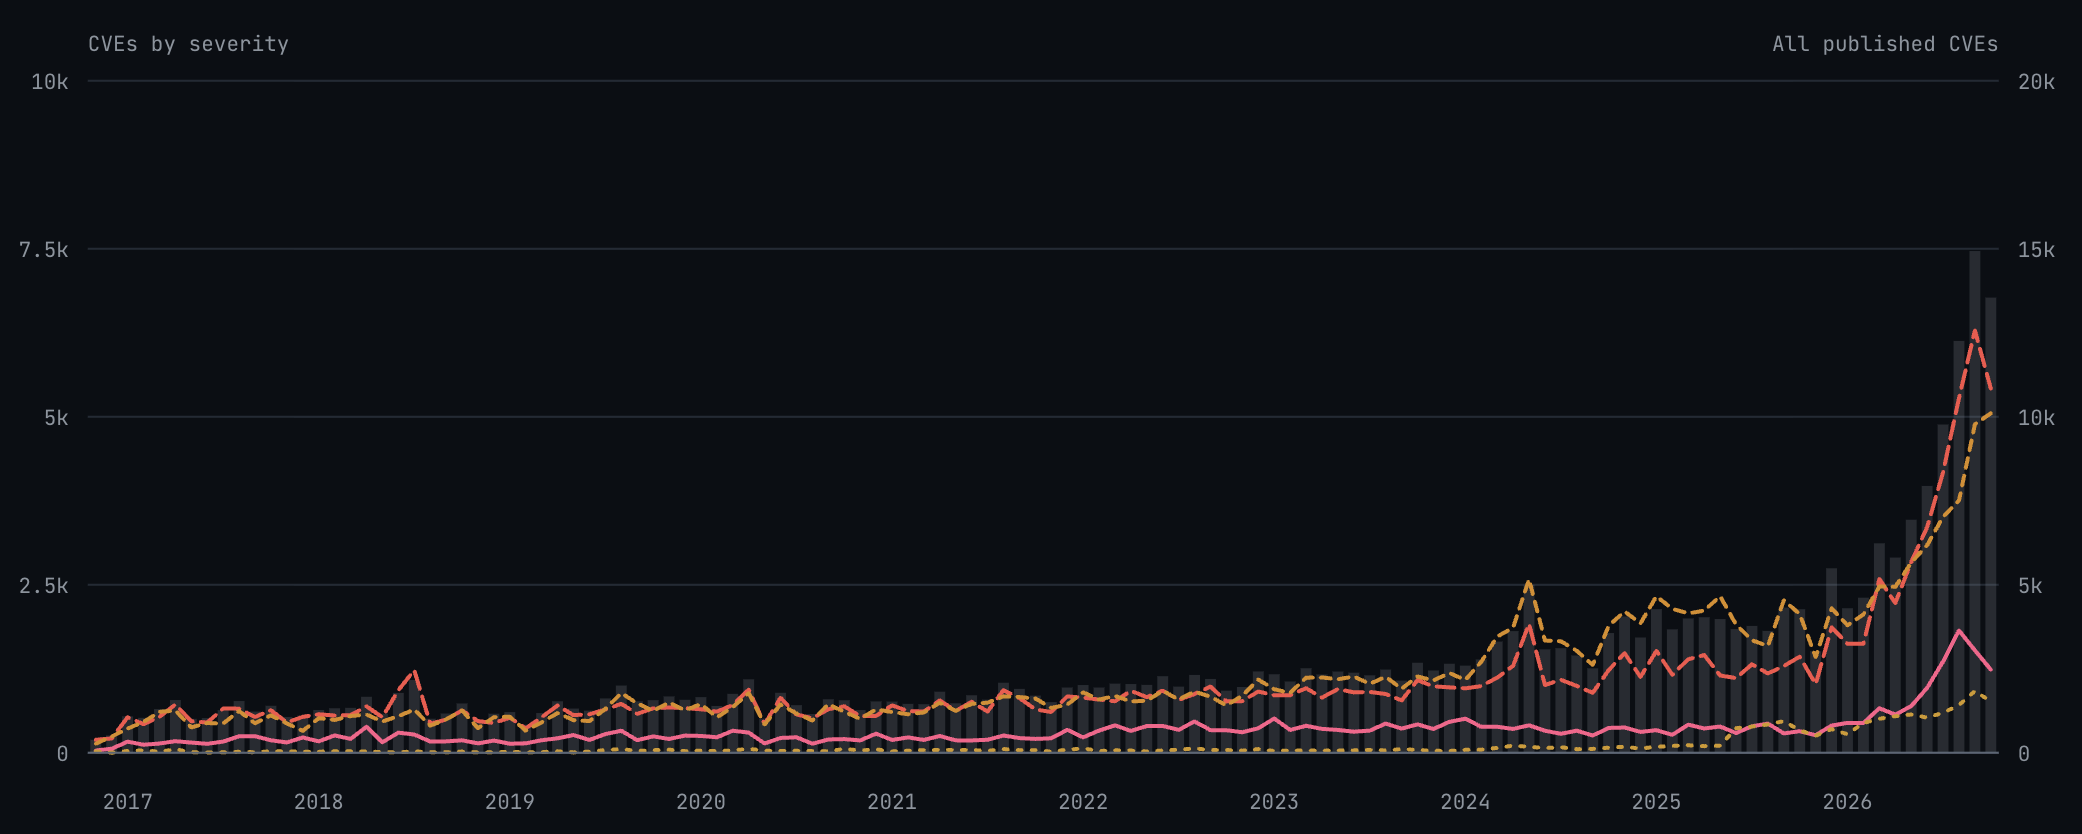
That's a problem across all technology scopes.
What can you do about it?
- Don't make it easy for bad actors to know what technoligies you are running.
- Keep internal inventory of your technologies and the vulnerabilities as they are announced
- Patch them as quickly as possible when new vulnerabilities match your tech inventory
- Scan your own code + apps for unknown vulnerabilities. The known vulnerabilities don't cover your code, you are 100% responsible for that. If you don't scan it for vulnerabilities from at least 2 perspectvies (code + outside in) you can get caught offguard when someone does it with malicious intent.
How we can help
- NewScan will show you what detectable technologies you have from an outside in perspective you have and how they were detected so that you can remove them.
- Our SAST product will inventory your technologies of scanned apps, if you dont already have them listed somewhere else.
- Our SAST product will check your dependencies and vulnerabilities for known CVEs
- SAST will inpsect your code while NewScan will give the outside in perspective. Together they fully cover your application from the internal and outside in perspective. They also work well together
**At a bare minimum download a free copy of NewScan to see what your app looks like from an outside bad actor perspective. **
We are focused on making peopels software safer from attacks. If we are missing something in this area let us know.